Blacklisted Passwords
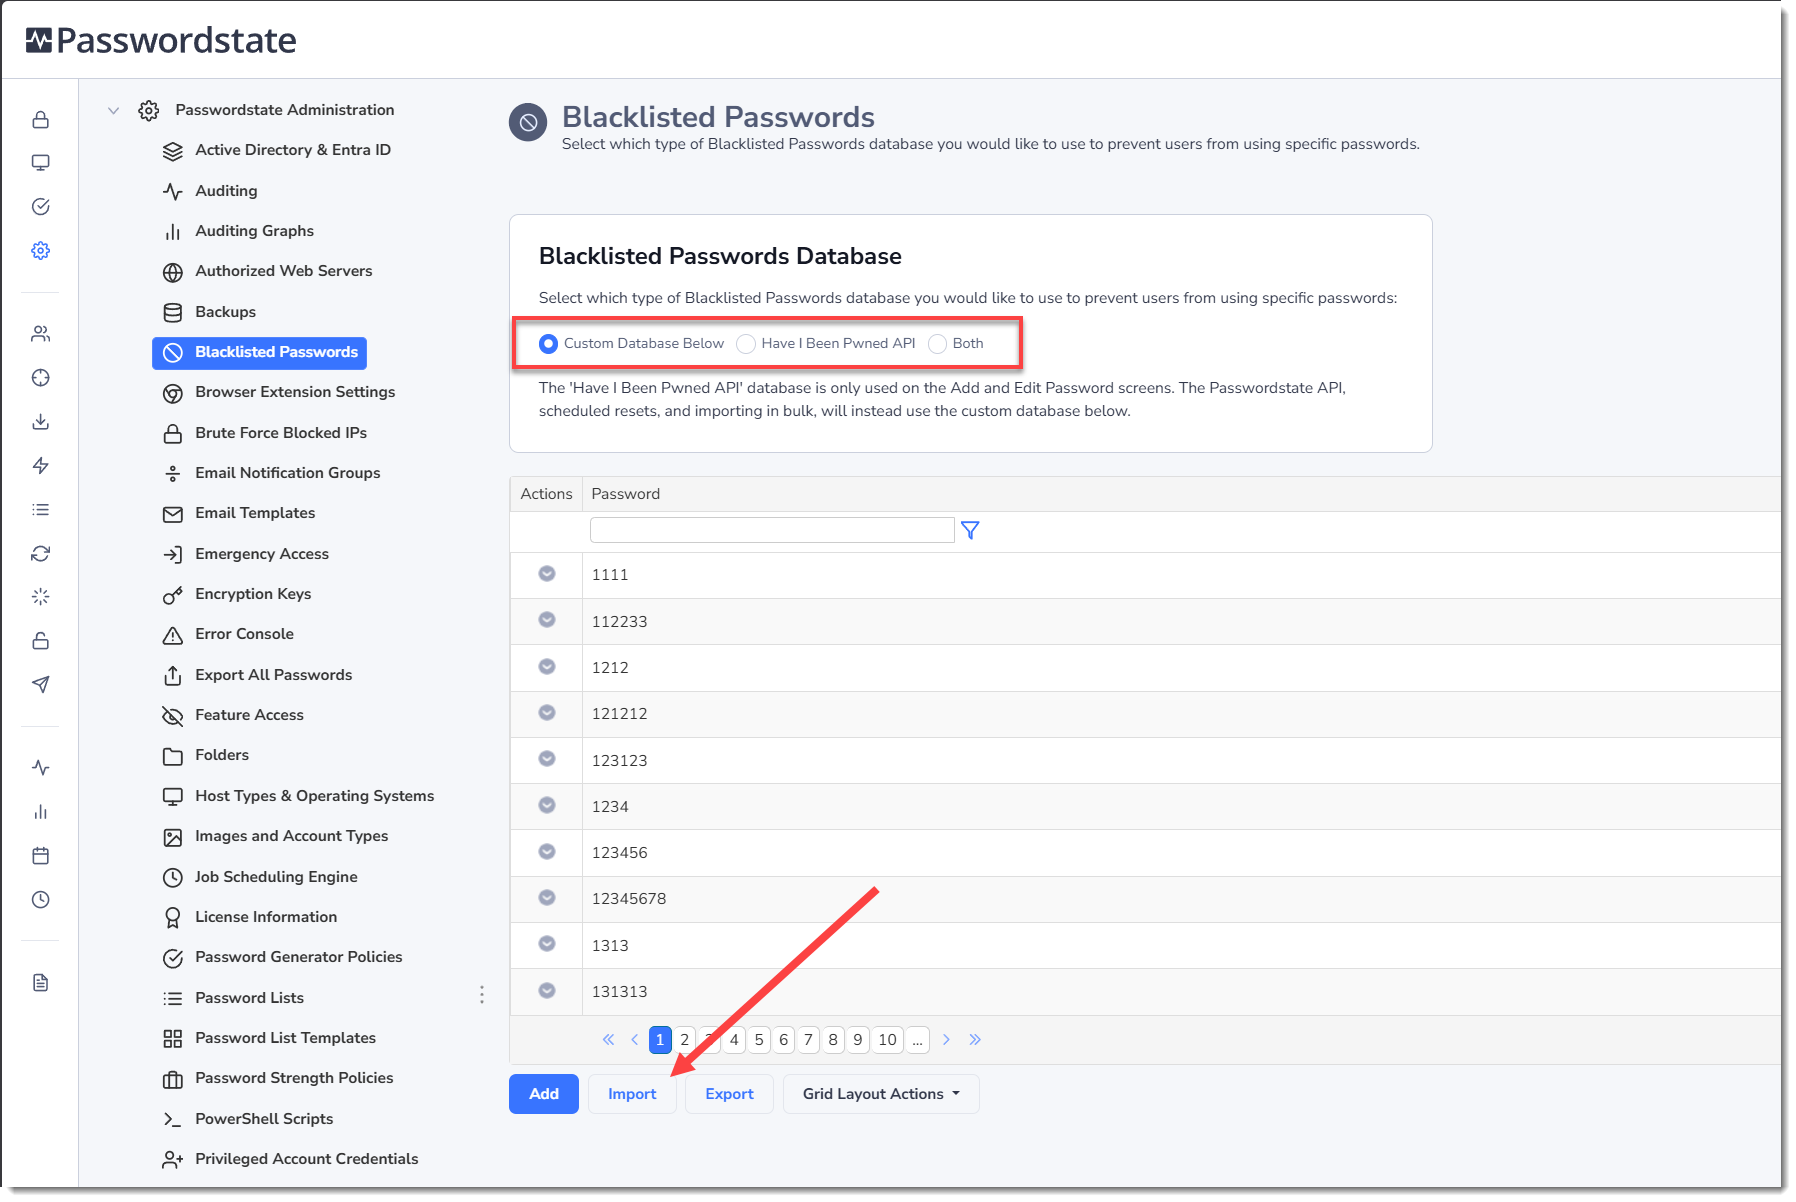
On the Blacklisted Passwords screen, there are three options available to prevent users from using certain passwords which are deemed to be 'Bad'.
You can either use the built-in custom Blacklisted Passwords database, or you can use the online 'Have I been Pwned' database from this site https://haveibeenpwned.com/, or you can use both.
'Have I been Pwned' is a list of known passwords from various security breaches across the globe. If using this feature, your web server hosting the Passwordstate must be able to make calls to the internet, specifically to the haveibeenpowned.com website.
Note 1: If you use the 'Have I been Pwned' database, this is only available on the Add and Edit Passwords screens. The Passwordstate API, scheduled resets, and importing in bulk, will instead use the Custom Bad Passwords database.
Note 2: If you use the 'Have I been Pwned' database, your Passwordstate web server must have access to the internet to query this API online. It can slow down performance of saving records on the Add/Edit screens, as it first needs to reach out to the Internet to perform the check.
Note 3: The 'Have I been Pwned' integration is both client and server based, depending on the feature used i.e. reports execute from the Passwordstate server, and UI buttons for checking a password status against haveibeenpwned.com are client based. For this reason, the 'Have I been Pwned' API must be allowed from the Passwordstate web server, and from user's desktops.
If required, you can also import multiple 'Blacklisted Passwords' into Passwordstate, via the Import button in the screenshot below.